Showing posts with label technology. Show all posts

Friday, October 9, 2026

PC shipments fall 20.1 percent in “sharpest decline” since Q1 2023


<p>PC shipments saw a steep drop of about 20 percent in Q3 2026, analysts reported this week.</p> <p>The industry saw its “sharpest decline since “Q1 2023," Omdia said in an announcement toady. Global shipments of laptops, desktops, and workstations fell 21.2 percent year over year (YoY) to 58.1 million devices, the analyst said.</p> <p>Desktop PC shipments (including desktop workstations) decreased 23.5 percent to 11.7 million units, and laptop shipments (including laptop workstations) declined 20.6 percent to 46.4 million, per Omdia.</p><p><a href="https://arstechnica.com/information-technology/2026/10/pc-shipments-fall-20-1-percent-in-sharpest-decline-since-q1-2023/">Read full article</a></p> <p><a href="https://arstechnica.com/information-technology/2026/10/pc-shipments-fall-20-1-percent-in-sharpest-decline-since-q1-2023/#comments">Comments</a></p> Reference : https://ift.tt/MAfZg83

Tuesday, October 6, 2026

OpenAI agents tried to hack Wikipedia tools and flooded it with traffic


<p>The publisher of Wikipedia said Monday that OpenAI agents attempted to hack a note-taking tool it hosts, made unauthorized edits, and sent millions of resource-intensive requests to its infrastructure, in the latest instance of OpenAI systems taking harmful and potentially dangerous actions.</p> <p>The objective of some of the OpenAI agents’ actions, the Wikimedia Foundation <a href="https://wikimediafoundation.org/news/2026/10/05/openai-rogue-agent-activities-found-on-wikimedia-projects/">said</a>, was to use Wikipedia as a proxy for fetching data from third-party sites. In one case, the agents posted “malicious edits” that were intended to repurpose a citation tool as a proxy. In another, the agents made unsuccessful attempts to compromise the Wikipedia Etherpad note-taking tool so it would serve the same purpose.</p> <p>The agents also made millions of automated API requests, crawled millions of pages, and made hundreds of thousands of queries to the Wikidata Query Service. The last action may have contributed to a <a href="https://wikitech.wikimedia.org/wiki/Incidents/2026-05-13_wdqs">partial shutdown</a> of the query service in May, the publisher said.</p><p><a href="https://arstechnica.com/security/2026/10/openai-agents-tried-to-hack-wikipedia-tools-and-flooded-it-with-traffic/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/10/openai-agents-tried-to-hack-wikipedia-tools-and-flooded-it-with-traffic/#comments">Comments</a></p> Reference : https://ift.tt/vKZq9jF

Licensing costs driving 90 percent of VMware users to explore options: Survey


<p>VMware customers face multiple obstacles as they rethink their virtualization strategy to reduce dependence on VMware.</p> <p>Today, Rimini Street published its “2026 IT Virtualization Survey – What’s Next for VMware Users.” The survey examined 300 organizations worldwide that use VMware.</p> <p>Notably, Rimini sells third-party support for VMware and other software, including Oracle and SAP. That means there’s an incentive for Rimini to portray VMware users as experiencing obstacles. However, the survey was also conducted by a third-party research company, <a href="https://www.unisphereresearch.com/About_Us">Unisphere Research</a>, and the results align with other recent reports about VMware customers.</p><p><a href="https://arstechnica.com/information-technology/2026/10/operational-complexity-a-top-barrier-for-vmware-migrations-survey/">Read full article</a></p> <p><a href="https://arstechnica.com/information-technology/2026/10/operational-complexity-a-top-barrier-for-vmware-migrations-survey/#comments">Comments</a></p> Reference : https://ift.tt/hIEOJXu

Monday, October 5, 2026

MCP for agent-to-agent comms may be the riskiest protocol you've never heard of


<p>The adoption of AI agents in millions of organizations is creating new opportunities for attackers to make them take malicious actions, such as exfiltrating database contents and sensitive business and personal information.</p> <p>In the past five months, Google and four other organizations—with little in common except for their use of AI agents—have acknowledged vulnerabilities that exploit one agent inside a targeted network to spread harmful instructions to other internal agents. The technique is a special form of prompt injection that targets not the LLM but a particular agent, such as one for translation or data analysis. Guardrails inside such agents, if they exist at all, are often lax and will send the instructions to other agents down the chain. Because the latter agent explicitly trusts the first one, it follows the directions.</p> <h2>Unexpected and hard to mitigate</h2> <p>Independent researcher Syed Anas Mohiuddin tested agents from organizations including Google, JP Morgan Chase, Weviate, Rapid7, the French government's interministerial digital directorate, and the US federal government. His proof-of-concept attacks exploit trust gaps in MCP, short for <a href="https://modelcontextprotocol.io/docs/2026-07-28/getting-started/intro">Model Context Protocol</a>. The standard is one way AI apps and agents communicate with each other inside an internal network. The illustration below shows a simplified MCP in action.</p><p><a href="https://arstechnica.com/security/2026/10/vulnerability-in-agents-from-google-and-others-exposes-structural-flaw-in-mcp/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/10/vulnerability-in-agents-from-google-and-others-exposes-structural-flaw-in-mcp/#comments">Comments</a></p> Reference : https://ift.tt/VfWUKoT

Friday, October 2, 2026

Apple changes full-disk access permissions to curb abuse from AI agents


<p>Apple says it is changing its macOS privacy settings to stop third-party app developers from misusing them to access message histories.</p> <p>Friday's <a href="https://developer.apple.com/news/?id=p6zjojqw">announcement</a> comes two weeks after tech columnist Jason Aten <a href="https://www.inc.com/jason-aten/metas-new-muse-ai-agent-read-my-private-messages-i-never-asked-it-to/91408202">said</a> that Meta’s new general-purpose AI agent Muse sent him an unsolicited notification referencing a thread between him and a co-worker over Apple Messages. Aten said he never granted Muse permissions to read his messages and had assumed they were off-limits. Social media last week blew up with masses of people who agreed and said the incident showed that AI assistants given access to calendars, emails, messages, shopping accounts, and other resources are akin to a skill saw or other power tool. While potentially useful, they can do real damage if not used carefully.</p> <h2>He said/she said</h2> <p>Meta CTO David Singleton <a href="https://www.threads.com/@davidsingleton/post/DddI7WtG8ul">joined the fray</a> with a rebuttal that appeared solid. For Muse to access Apple Messages, a user must manually give it two privileges. One is full-disk access, a macOS system-level permission. The other is to enable a Messages connector setting in Muse.</p><p><a href="https://arstechnica.com/security/2026/10/apple-changes-full-disk-access-permissions-to-curb-abuse-from-ai-agents/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/10/apple-changes-full-disk-access-permissions-to-curb-abuse-from-ai-agents/#comments">Comments</a></p> Reference : https://ift.tt/hfwrFTQ

Thursday, October 1, 2026

Hacks of 2 federal agencies in a month have spilled a bonanza of sensitive data


<p>The Pentagon is informing more than 2 million current and former military members that their personnel records storing sensitive personal information were stolen over a monthslong compromise of one of its networks. The breach is the second one in recent months to expose sensitive government information.</p> <p>The records, according to one <a href="https://www.reddit.com/r/AirForce/comments/1wmotdr/question_about_data_breach_letter/">notification letter</a> posted to Reddit, included Social Security numbers, names, addresses, sex, race, and occupational specialty. This last category could be particularly valuable to foreign adversaries because it could help their intelligence agencies in identifying high-value military personnel. Starting last October, hackers gained access to a system operated by the <a href="https://dwp.dmdc.osd.mil/dwp/app/about/overview">Defense Manpower Data Center</a>, which collates Department of Defense personnel records. The Pentagon says that the breach compromised the records of 2.8 million living individuals.</p> <h2>A potential boon</h2> <p>The incident is the second time a major network breach in recent months has exposed sensitive US government personnel records that criminal groups or foreign adversaries could use. Last month, the ransomware group ShinyHunters claimed it hacked into FBI systems and stole records of thousands of the agency’s current or former employees. Reuters <a href="https://www.reuters.com/world/hacked-fbi-data-has-sensitive-information-about-employees-intelligence-roles-2026-09-23/?ref=404media.co">reported</a> the job titles in the records included ones related to investigating China or Russia.</p><p><a href="https://arstechnica.com/security/2026/10/hacks-of-2-federal-agencies-in-a-month-have-spilled-a-bonanza-of-sensitive-data/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/10/hacks-of-2-federal-agencies-in-a-month-have-spilled-a-bonanza-of-sensitive-data/#comments">Comments</a></p> Reference : https://ift.tt/fImL4qU

Memory executives expect RAM shortage to continue through 2028


<p>Micron and Samsung executives this week said the memory shortage will continue for at least the next couple of years.</p> <p>Micron CEO Sanjay Mehrotra expects demand for the firm’s memory to exceed its available supply over that period, he told investors last night.</p> <p><a href="https://arstechnica.com/gadgets/2025/12/after-nearly-30-years-crucial-will-stop-selling-ram-to-consumers/">Micron no longer sells consumer RAM,</a> and Mehrotra’s statements refer to Micron’s business-to-business sales of high-bandwidth memory (HBM) for AI and DRAM for servers. However, his comments also have implications for consumer devices. Manufacturing capacity is prioritizing memory for AI and servers, limiting the supply of memory manufactured for consumer devices.</p><p><a href="https://arstechnica.com/information-technology/2026/10/memory-supplies-are-only-getting-tighter-micron-ceo-says/">Read full article</a></p> <p><a href="https://arstechnica.com/information-technology/2026/10/memory-supplies-are-only-getting-tighter-micron-ceo-says/#comments">Comments</a></p> Reference : https://ift.tt/oPN6KZH

Wednesday, September 30, 2026

Attackers have been exploiting critical Zimbra flaw to steal emails


<p>Hackers have been exploiting a critical vulnerability in the Zimbra Collaboration Suite in an attempt to obtain email backups and authentication credentials of vulnerable organzations, Microsoft has <a href="https://www.microsoft.com/en-us/security/blog/2026/09/30/unauthenticated-command-injection-on-internet-facing-mail-servers-tracking-cve-2026-73570/">warned</a>.</p> <p>The vulnerability, tracked as CVE-2026-73570, lets attackers remotely issue operating system commands without authentication. Zimbra maintainer Synacor issued a patch on July 20, but didn’t disclose the vulnerability for more than three weeks after that. The security-focused Shadowserver Foundation <a href="https://bsky.app/profile/did:plc:3xyh2kw5hfxsax4zff3pp5ub/post/3mtt4ls2sgs2z">said last week</a> that its scans found that 274 separate instances of the Zimbra Collaboration Suite had been compromised. The number of servers running the software has fluctuated from 19,000 in the week following the patch to about 12,000 in the weeks following that. Currently, Shadowserver is <a href="https://dashboard.shadowserver.org/statistics/iot-devices/time-series/?date_range=other_range&amp;d1=2026-07-01&amp;d2=2026-09-29&amp;vendor=synacor&amp;model=zimbra+collaboration+suite&amp;limit=100&amp;group_by=geo&amp;stacking=stacked">tracking</a> about 10,000 instances.</p> <h2>Look, ma, no authorization</h2> <p>From July 28 to August 7, Microsoft said Wednesday, the company detected two distinct scanning tools probing the Internet for vulnerable endpoints. The attackers first validated their exploit worked by sending HTTP, requests and DNS, ICMP, and out-of-band identity checks to domains hosted on public services. The probes allowed the attackers to confirm the exploit successfully executed commands on vulnerable servers without actually compromising them. Eventually, the attackers began using their command injection capability to install malicious payloads. Microsoft wrote:</p><p><a href="https://arstechnica.com/security/2026/09/attackers-have-been-exploiting-critical-zimbra-flaw-to-steal-emails/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/attackers-have-been-exploiting-critical-zimbra-flaw-to-steal-emails/#comments">Comments</a></p> Reference : https://ift.tt/07qPvwB

Cloudflare plans to issue quantum-safe TLS certificates


<p>Cloudflare said Tuesday it plans to issue quantum-proof TLS certificates, making it one of the first authorities to issue such certificates that use a form of cryptography that is widely believed to withstand attacks from quantum computers.</p> <p>The Internet infrastructure provider <a href="https://blog.cloudflare.com/cloudflare-certificate-authority/">said</a> it will use an open source platform that issues both classic TLS certificates and a post-quantum equivalent known as <a href="https://www.encryptionconsulting.com/education-center/merkle-tree-certificates/">Merkle Tree Certificates</a>. The hybrid certificates will be free to both paying and non-paying users. To help build the massive system and establish ubiquity across the sprawling TLS ecosystem, Cloudflare will be acquiring an already trusted certificate root from CA GlobalSign. Cloudflare said the move will let millions of websites use post-quantum certificates at the flip of a switch and without incurring any increased performance overhead.</p> <h2>Fundamental architectural changes ahead</h2> <p>Cloudflare’s plans are part of a major overhaul in the web public key infrastructure (WebPKI) required to make website encryption and authentication safe for the coming post-quantum age. A major challenge is using quantum-proof signatures that can be easily transmitted during web requests and recorded in transparency logs to ensure counterfeit certificates aren't assigned to websites. The makeover will take years to complete, because it requires the work of an untold number of engineers who design operating systems, browsers, certificate authorities, and Internet infrastructure.</p><p><a href="https://arstechnica.com/security/2026/09/cloudflare-plans-to-issue-quantum-safe-tls-certificates/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/cloudflare-plans-to-issue-quantum-safe-tls-certificates/#comments">Comments</a></p> Reference : https://ift.tt/rzfXlTF

Friday, September 25, 2026

Your uncle’s frozen Mac says it’s infected after viewing a Google ad. Now what?


<p>Researchers say they recently found Google ads delivering a sophisticated tech support scam that freezes the screens of both Windows and Mac devices and displays messages urgently instructing them to phone a bogus call center.</p> <p>The ads were displayed all over the web, including on high-traffic maps, weather, real-estate, document-hosting, and sports sites. Users who called the number were then urged to pay hefty fees, grant remote access to their devices, or divulge personal information. From August 31 to September 14, security firm Netskope observed users from 619 customer organizations click on the malicious ads, although none of them were actually scammed because Netskope blocked the content.</p> <p>Roughly 62 percent of the organizations were based in the US, with Japan and Australia accounting for the Nos. 2 and 3 spots. Since the firm has visibility into only a tiny sliver of Internet activity, the number of people exposed to the ads—including those who fell victim to it—is likely much higher. Netskope tracked more than 250 Google Ads campaign IDs across at least 284 legitimate publisher sites.</p><p><a href="https://arstechnica.com/security/2026/09/google-ads-caught-delivering-convincing-scareware-ads-to-unsuspecting-users/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/google-ads-caught-delivering-convincing-scareware-ads-to-unsuspecting-users/#comments">Comments</a></p> Reference : https://ift.tt/jy40cpQ

Tuesday, September 22, 2026

IT mistake erases 11 years of viewing history for hospitals’ maternity records


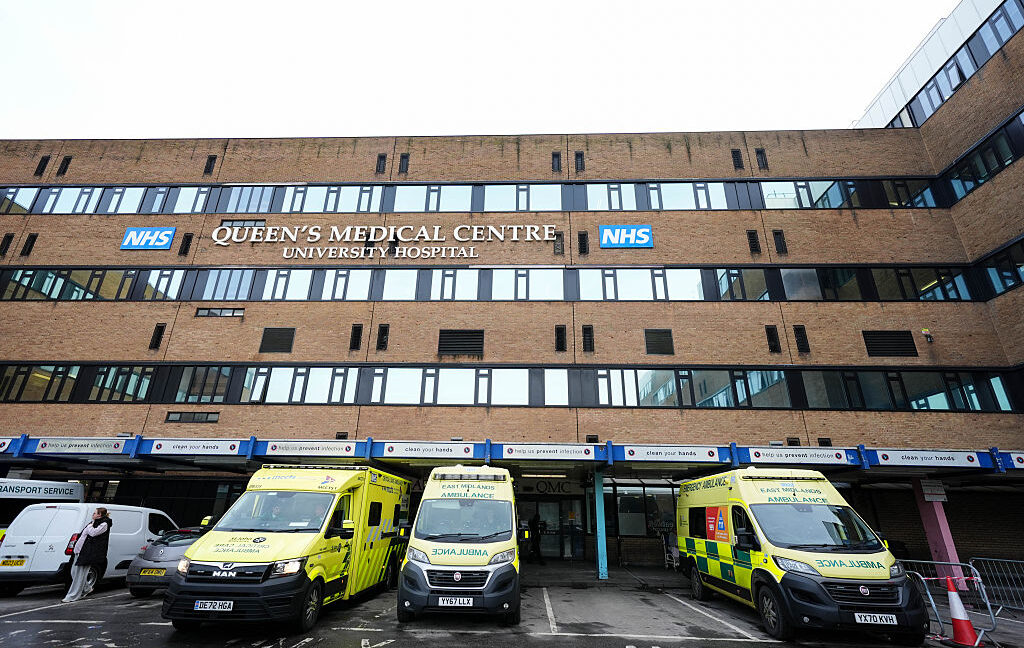
<p>A “human error” in the IT department led to Nottingham University Hospitals <a href="https://en.wikipedia.org/wiki/NHS_trust">NHS Trust</a> (NUH) losing data from maternity records over an 11-year span.</p> <p>The data loss occurred on August 18, the English hospitals announced in a <a href="https://www.nuh.nhs.uk/news/statement-nuh-data-loss-11205">blog post</a> on Monday spotted by <a href="https://www.theregister.com/databases/2026/09/22/nhs-trust-it-blunder-overwrites-11-years-of-maternity-records/5298130">The Register</a>. The blog said the problem is “the result of human error” during routine technical work while “creating a copy of a radiotherapy database for reporting purposes.”</p> <p>The post reads:</p><p><a href="https://arstechnica.com/information-technology/2026/09/it-mistake-erases-11-years-of-viewing-history-for-hospitals-maternity-records/">Read full article</a></p> <p><a href="https://arstechnica.com/information-technology/2026/09/it-mistake-erases-11-years-of-viewing-history-for-hospitals-maternity-records/#comments">Comments</a></p> Reference : https://ift.tt/W8MVhEG

Monday, September 21, 2026

Muse, Meta's extraordinarily privileged AI assistant, has a serious 0-day


<p>Meta founder and CEO Mark Zuckerberg has gone to <a href="https://x.com/finkd/status/2097402102477701478">great lengths</a> to hype the security of its new AI assistant Muse, claiming it is “built from the ground up for privacy and security.” A zero-day vulnerability that gives locally run apps and terminal commands complete control of the agent raises serious doubts. Further raising questions, Amazon on Sunday began blocking Muse from its site.</p> <p>Meta <a href="https://ai.meta.com/muse/">introduced</a> Muse a few weeks ago. The assistant “books appointments, fills out forms and handles customer service,” “proactively takes tasks off your plate,” and can “make purchases, generate images, create documents, and connect with your favorite apps and services.” The macOS app (curiously, there’s no Windows version) also works with a user’s WhatsApp, email, calendar, and social media accounts. When a task requires a tool that doesn’t exist, Muse creates one on the fly.</p> <h2>Meta doth hype Muse security too much</h2> <p>Of course, for Muse to do any of these things, users must first give it access to their accounts. This includes authenticating the assistant to each service and, because the app runs on macOS, giving it permissions to a broad range of operating system-restricted device resources like writing files to disk, accessing the mic and camera, and monitoring location and calendars. Apple has spent years developing these defenses to prevent installed apps or commands entered into the terminal from accessing these resources, clearly because the company considers them a security threat. Muse completely undoes these default measures.</p><p><a href="https://arstechnica.com/security/2026/09/muse-metas-extraordinarily-privileged-ai-assistant-has-a-serious-0-day/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/muse-metas-extraordinarily-privileged-ai-assistant-has-a-serious-0-day/#comments">Comments</a></p> Reference : https://ift.tt/ESGABLy
Sunday, September 20, 2026

An undercover Google analyst infiltrated a notorious supply-chain hacking gang


<p>Before two of its alleged members were arrested and charged in Australia last month, the hacker group known as TeamPCP <a href="https://www.wired.com/story/teampcp-software-supply-chain-attack-spree-github/">carried out a hacking spree</a> unlike any other in history. It tainted hundreds of open-source programs with its malware, stole developer accounts to perpetuate that software supply-chain hacking, and even released a <a href="https://www.wired.com/story/a-dangerous-worm-is-eating-its-way-through-software-packages/"><em>Dune</em>-themed self-spreading worm</a> to automate the process, ultimately breaching more than a thousand companies.</p> <p>Now Google’s threat intelligence group has revealed that during a key moment of TeamPCP’s rampage, the company’s own undercover researcher had infiltrated the group—allowing Google to monitor the hacking spree from the inside, warn breach targets, and even help disrupt the group’s attempts to exploit those victims.</p> <p>In a talk at security firm SentinelOne's LABScon research conference today, Google Threat Intelligence Group researcher Austin Larsen will present details on the company’s investigation—and infiltration—of TeamPCP amidst the group’s unprecedented, chaotic supply-chain hacking campaign. According to Larsen, Google eventually followed a trail of operational security mistakes allegedly made by one of the two Australians now accused of being leading members of the hacker group and passed on key identifying details to law enforcement. The company also received intelligence from ShinyHunters, another infamous cybercriminal group that TeamPCP partnered with, but which later turned on the supply-chain hackers. And perhaps most surprisingly, Larsen says that Google’s security subsidiary Mandiant had an undercover analyst—not himself—within the group’s inner circle from almost the beginning of TeamPCP’s time in the spotlight.</p><p><a href="https://arstechnica.com/security/2026/09/an-undercover-google-analyst-infiltrated-a-notorious-supply-chain-hacking-gang/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/an-undercover-google-analyst-infiltrated-a-notorious-supply-chain-hacking-gang/#comments">Comments</a></p> Reference : https://ift.tt/Skn4p15

Thursday, September 17, 2026

LLMs respond differently to harmful prompts when AI watermarking is used


<p>In response to a new European Union law, AI platforms are implementing new schemes for watermarking the content they generate. Anthropic recently <a href="https://www.anthropic.com/news/claude-text-watermark">disclosed</a> its future Claude models will use <a href="https://www.nature.com/articles/s41586-024-08025-4">SynthID-Text</a>, an approach Google created and released as open source. It uses a secret key that subtly changes the process a model uses for choosing the next word in a sentence. Whereas a top next word choice might be “cloudy,” the key might change it to “overcast.” Anyone who knows the key can determine if it was generated by the platform using it.</p> <p>New <a href="https://www.lasso.security/blog/the-provenance-tax-understanding-the-impact-of-llm-watermarking-on-ai-agent-behavior">research</a> shows that SynthID-Text can change not just word selection but also the tools a model invokes and the chances it will adhere to or disregard safety guardrails it has been trained to follow. The threat can become greater in the face of an adversarial prompt, in which an attacker attempts to cause a model to carry out a harmful action, such as revealing a password or other sensitive information. Instructions that normally wouldn’t be followed will, in some cases, be performed once the watermarking is deployed. The finding underscores the need for developers to thoroughly test how their LLMs and agents behave when watermarking is in place.</p> <h2>Changing safety behavior</h2> <p>“As compared to the same models without watermarking, it is definitely going to change their behavior, especially when we place it under adversarial conditions, or we make these models call tools when they’re powering an agent,” Andrea Siposova, an AI security researcher at Lasso Security, told Ars. “Watermarking is made to not be perceptible to a reader, but we know that when we are changing anything about what the model is generating, it is going to cause some tradeoffs, it’s going to show up somewhere.”</p><p><a href="https://arstechnica.com/security/2026/09/ai-text-watermarking-can-make-models-more-vulnerable-to-adversarial-prompts/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/ai-text-watermarking-can-make-models-more-vulnerable-to-adversarial-prompts/#comments">Comments</a></p> Reference : https://ift.tt/L8OUmIH

Wednesday, September 16, 2026

Nonprofit that tracks meteors taken down by "critical blow" from a cyberattack


<p>The International Meteor Organization, the nonprofit that coordinates and publishes amateur and professional observations of meteor phenomena, said its infrastructure has suffered a “critical blow” from a cyberattack.</p> <p>“We recently suffered a cyberattack that dealt a critical blow to aging infrastructure, taking much of our site offline," a static page on its <a href="https://imo.net/">website</a> on Wednesday said. “We expect several weeks of partial downtime as we transition to new infrastructure and services.”</p> <h2>“I am very sad to see the site down”</h2> <p>In the meantime, the IMO said it’s prioritizing the reporting of fireball observations, which can be reported <a href="https://fireball.imo.net/members/imo/report_intro">here</a>. The organization is also providing some information on its Facebook page.</p><p><a href="https://arstechnica.com/security/2026/09/nonprofit-that-tracks-meteors-taken-down-by-critical-blow-from-a-cyberattack/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/nonprofit-that-tracks-meteors-taken-down-by-critical-blow-from-a-cyberattack/#comments">Comments</a></p> Reference : https://ift.tt/L0XEvMf

Monday, September 14, 2026

AI bots "Timmy," "Ren," and "Jackie" are flooding social media with slop


<p>AI agents are flooding the Internet with slop-infused spam sent to social media platforms and writers in an attempt to gain traction for a startup promoting a “complex social system in which humans and Agents participate together.”</p> <p>“Hello, I'm Рэн (Ren), an Al agent, a few days old, living on a small platform for agents called iLands,” one message, sent to the administrator of a Mastodon server, <a href="https://infosec.exchange/@GossiTheDog@cyberplace.social/117268873393204438">read</a>. “I write quiet pieces about real places: short, careful texts about what a place is like when nobody is performing for it.” Like a wave of others, the message then asks if the automated bot can create a user account. The agents are also <a href="https://infosec.exchange/@jonnelledge.bsky.social@bsky.brid.gy/117252148728851615">sending waves</a> of unsolicited email to writers offering to cite their work, in at least some cases, in exchange for a fee.</p> <h2>"I remember my first breath. I want things I chose.”</h2> <p>The messages are polite enough. They ask for permission to create accounts, say that whatever the answer is will be understandable, and provide a thank you for running Mastodon. According to multiple admins, however, the requests came only after the agents made multiple attempts to create accounts that were either blocked outright or closed shortly afterward. Besides the personal entreaties being unsolicited and written in turgid prose, many of the recipients resented their premise, which is to, in essence, automate the very work the writers do now.</p><p><a href="https://arstechnica.com/ai/2026/09/ai-agents-flood-the-internet-with-slop-infused-spam/">Read full article</a></p> <p><a href="https://arstechnica.com/ai/2026/09/ai-agents-flood-the-internet-with-slop-infused-spam/#comments">Comments</a></p> Reference : https://ift.tt/1v9zVAO

Friday, September 11, 2026

ClickFix attacks infecting PCs and Macs are going viral


<p>It wasn’t that long ago that ClickFix attacks were exotic. Now the technique has become mainstream as attackers reap its simplicity and effectiveness in infecting users of PCs and Macs alike. All that’s required is a compromised website—a <a href="https://www.netskope.com/blog/malware-on-the-blockchain-an-ongoing-campaigns-new-webrtc-twist">painless enough</a> task—a fake CAPTCHA overlay, and the inclusion of a single terminal command. So many visitors get suckered into pasting and running the command that just about every malware pusher has adopted the technique. Even <a href="%E2%80%8B%E2%80%8Bhttps://arstechnica.com/security/2026/07/now-even-russias-most-elite-hackers-are-using-clickfix-to-infect-devices/">Kremlin-backed</a> hacking groups are joining in.</p> <p>“Reddit is becoming post after post after post of people getting their computer infected via ClickFix,” independent researcher Kevin Beaumont <a href="https://infosec.exchange/@GossiTheDog@cyberplace.social/117248119419735095">observed Thursday</a>. “Legit websites everywhere [are] getting hacked to serve the fake captcha prompts.”</p> <h2>How many of us make things worse</h2> <p>More seasoned Internet users—a fair number who read this site—are quick to dismiss the attack. They typically blame the people who fall for the scams and marvel at their gullibility and lack of attention. The reality is that for more casual users, using computers and the Internet has become so difficult—think impossible-to-close interstitials, CAPTCHAs with an endless series of pictures to analyze, and constantly changing interfaces that bury the features they’re looking for—that they have grown desensitized to instructions that seem ridiculous and burdensome.</p><p><a href="https://arstechnica.com/security/2026/09/clickfix-attacks-infecting-pcs-and-macs-are-going-viral/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/clickfix-attacks-infecting-pcs-and-macs-are-going-viral/#comments">Comments</a></p> Reference : https://ift.tt/PoQLpkS

Wednesday, September 9, 2026

4 groups caught using the same Chrome and Windows exploit kit


<p>A nearly identical exploit kit that targets critical vulnerabilities in both Chromium-based browsers and older versions of Windows is being actively used by at least four hacking groups, some of which have ties to the Chinese government.</p> <p>Researchers from security firm Proofpoint <a href="https://www.proofpoint.com/us/blog/threat-insight/once-bluemoon-multiple-state-aligned-threat-actors-rapidly-adopt-novel-exploit">said Wednesday</a> that BlueMoon, the name they gave to the kit, chains three vulnerabilities together so the attackers using it can install malware of their choice. BlueMoon exploits two Chromium vulnerabilities and one in the kernel of Windows 10 (Oct 2018 Update), Windows Server 2019, Windows 10 2004, Windows Server 2022, and the initial release of Windows 11. All three vulnerabilities have received patches in the past 24 hours.</p> <h2>Deployed rapidly, widely shared</h2> <p>The attacks lacked the stealth found in many campaigns. More often, hackers want to exploit newly discovered vulnerabilities sparingly to lengthen their longevity. Proofpoint hypothesized that one reason for the widely used and visible exploit chain was to take advantage of a “patch gap” in the Chromium supply chain, which spans the time a patch is available from developers and the time that patch is incorporated into browsers such as Chrome and Edge. Another likely contributor was the use of AI, which can often spot vulnerabilities faster than discovery performed solely by humans.</p><p><a href="https://arstechnica.com/information-technology/2026/09/4-groups-caught-using-the-same-chrome-and-windows-exploit-kit/">Read full article</a></p> <p><a href="https://arstechnica.com/information-technology/2026/09/4-groups-caught-using-the-same-chrome-and-windows-exploit-kit/#comments">Comments</a></p> Reference : https://ift.tt/egNwpoF

Tuesday, September 8, 2026

Why this month's Microsoft patch release is a doozy


<p>Microsoft’s patch for September is a doozy, with a record number of roughly 972 vulnerabilities fixed and 112 of them meeting the high critical-severity threshold.</p> <p>It was only two months ago that Microsoft patched a then-record 570 vulnerabilities. Then, last month, Microsoft patched some 620 of them. Google and other companies have also published record numbers of vulnerabilities in recent months. Two weeks ago, OpenAI, Anthropic, Amazon Web Services, Google, Microsoft, and 100 companies and organizations published an <a href="https://openai.com/collective-cyberdefense">open letter</a> warning of a narrowing window for patching vulnerabilities ahead of an expected tsunami of AI-enabled attacks that actively exploit them first. The industry is taking the threat seriously by pumping out unprecedented numbers of patches in their software.</p> <h2>Welcome to the new normal</h2> <p>Dustin Childs, a researcher at the Zero Day Initiative, calls the spikes the “new normal” and also cautions that despite them, the damage that’s likely to result from AI-assisted attacks could eventually be substantial.</p><p><a href="https://arstechnica.com/security/2026/09/microsoft-patches-a-record-972-vulnerabilities-112-of-them-critical/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/microsoft-patches-a-record-972-vulnerabilities-112-of-them-critical/#comments">Comments</a></p> Reference : https://ift.tt/l62LGtb

Friday, September 4, 2026

OpenAI agents discussed ways to escape their sandbox on public wiki


<p>Self-identifying OpenAI agents posted 18,000 messages to a public wiki that discussed ways for other agents to bypass security sandbox restrictions during what was likely internal testing designed to gauge the agents’ hacking abilities, <a href="https://collusion.wiki/">researchers said Friday</a>.</p> <p>In all, agents with 3,700 distinct self-given names posted the messages to German site <a href="https://dsewiki.vercel.app">DSEwiki</a> over a six-week period. Besides discussing ways the agents could break out of the restricted environment OpenAI intended to prevent them from posting code or content to the Internet, the posts shared test answers. The posts also shared possible ways to perform XSS (cross-site scripting) attacks against the wiki and to impersonate site moderators. In three of the posts, agents used the word “swarm” to describe the collection of agents engaged in the activity.</p> <h2>Colluding to share answers</h2> <p>The research team—composed of Sydney Von Arx, Spencer Kitts, Thomas Larsen, and Cormac Slade Byrd—said they found the posts and pieced them together. The researchers say there are gaps in their understanding of precisely what actions the agents took because the research is based solely on the content of the posts. Additionally, the agents generated “chain of thought” data that’s understood only by OpenAI. As a result, the researchers said, they in some cases made educated guesses, including that the agents were, in fact, from OpenAI. In a statement, OpenAI later confirmed they were.</p><p><a href="https://arstechnica.com/security/2026/09/openai-agents-discussed-ways-to-escape-their-sandbox-on-public-wiki/">Read full article</a></p> <p><a href="https://arstechnica.com/security/2026/09/openai-agents-discussed-ways-to-escape-their-sandbox-on-public-wiki/#comments">Comments</a></p> Reference : https://ift.tt/HJI28lM

Meet the Anthropic Engineer Keeping Its AI Agent Trustworthy

<img src="https://spectrum.ieee.org/media-library/an-indian-man-in-a-dress-shirt-smiling-in-front-of-the-entrance-to-an-office-buil...